

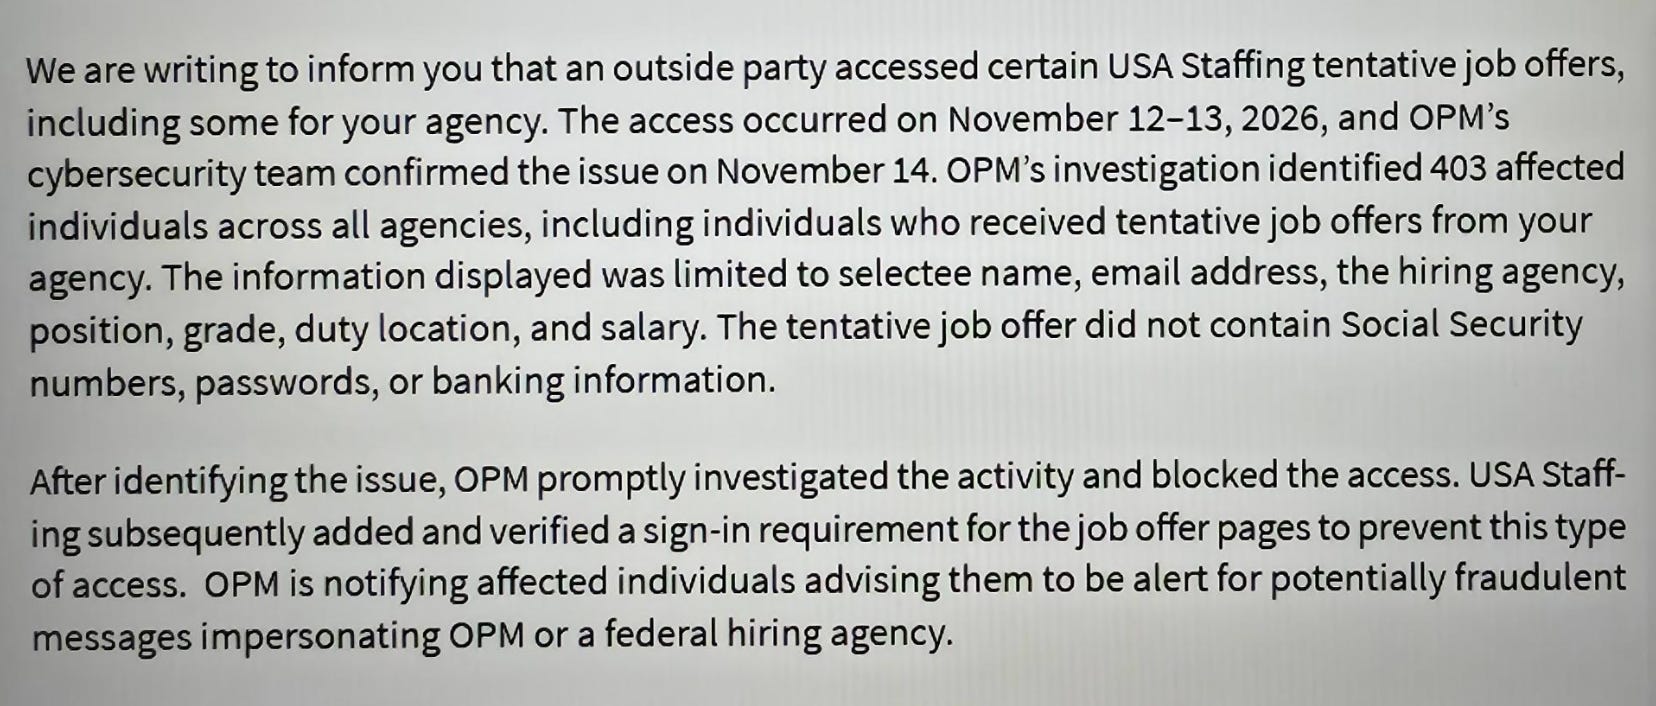
On Thursday, November 19th, multiple people at USA Staffing received an email from the Office of Personnel Management (OPM) informing them that an outside third party had accessed 403 tentative job offers across multiple agencies which included selectee names, emails, hiring agencies, position, grade, duty location, and starting salary.
According to the email, part of which can be seen below (signature blocks have been removed to protect anonymity), the breach took place on November 12th and 13th. For reference, the global Microsoft outage began November 12th, and the FAA ground stop began November 13th. There is no indication this breach of OPM is tied to any other outage or incident that happened that weekend, however.
While there were multiple government and corporate systems issues that weekend, the OPM breach has not been previously reported.
The OPM cybersecurity team confirmed the breach on November 14th, investigated, and blocked the access, according to the email. Those effected have been notified by the agency, and USA Staffing has added a sign-in requirement to prevent this type of access in the future.
If you’re a government employee or whistleblower and would like to contact me to publish information or refer you to an attorney, please contact me on Signal at muellershewrote.23. I will keep you anonymous.
We are so screwed.
I can’t read the monthly invoice from my HOA without 2 factor ID but personal contact details with job & salary info from multiple federal agencies? Cool cool… Republicans sure are good at running government like a bizness (long as it’s Madoff Investments or Crazy Vic’s Vape & Lo Price Cell Phones)
[edited to change “I’d” to “ID” - thanks iPhone!]